Log inSkip to main contentSkip to sidebar
IMPORTANT: JAC is a Public system and anyone on the internet will be able to view the data in the created JAC tickets. Please don’t include Customer or Sensitive data in the JAC ticket.
Organization audit log: For changes to product access groups, show the affected users
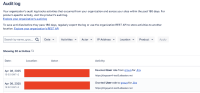
The organization audit log shows events for granted/removed product access roles from group. Example:
However, the org. audit log doesn't indicate which users are affected by the changes
Suggested Solution
When a group is granted/removed from the list of product access groups, list the affected user accounts in the "container" field or data field for the relevant audit log event
This logic can be also applied to group deletions
Why this is important
When an org. admin makes changes to product access groups, it's not clear from the audit log alone which end users are affected by a change to the product access groups
In the screenshot above, we can see that product access for a group has been granted, and then revoked - the org. audit log doesn't show which users are affected by the changes and have lost/gained product access
Workaround
No known workarounds, when a workaround is found - the workaround will be added here
Suggestion


Page Loading...